[Library Network] Conditions of Use and Licensing Restrictions for E-Resource
投稿日 2026-08-03 | カテゴリ: Library NetworkProhibited Actions When Using Electronic Resources
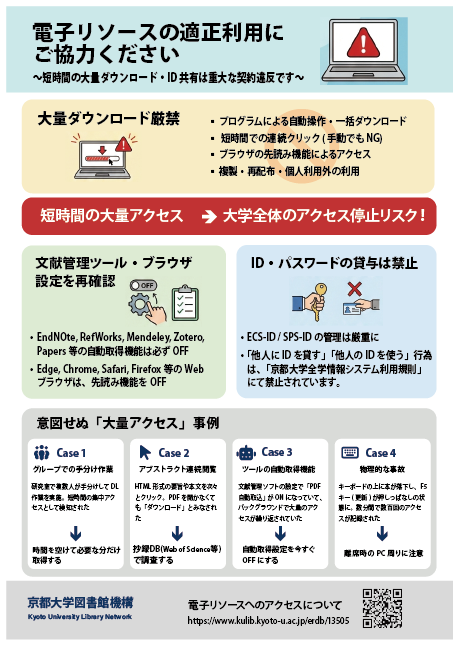
Mass Downloading Strictly Prohibited
- Automated operations or bulk downloads using programs
- Rapid consecutive clicks (prohibited even manually)
- Access via browser prefetch functions
- Copying, redistribution, or use beyond personal purposes
Cases of Unintentional "Excessive Access"
Cases where actions are considered "attacks" by system specifications are increasing, even without malicious intent.
Multiple people in a lab divided download tasks manually. Since the access source (university IP) was the same, it was detected as concentrated access in a short period.
Clicking through HTML abstracts and full texts one after another. Even without opening PDFs, the request frequency to the server was considered "downloading".
The "auto-import PDF" setting in reference management software was ON, causing repeated mass access in the background.
A book fell on the keyboard, holding down the F5 key (refresh). Hundreds of accesses were recorded in just a few minutes.
Essential! Settings Review Checklist
Reference Management Software (Turn OFF Auto-DL)
Prevent unintended background communication.
| Paperpile | Settings > Storage & Sync OFF "Automatically download PDFs" |
|---|---|
| EndNote Click Mendeley | Disable the extension or uncheck "Automatically add PDFs" in settings. |
| Zotero | Do not run "Find PDF" on multiple selections. Turn OFF Connector proxy settings when off-campus. |
| ReadCube | Do not use "LOCATE PDF" on multiple selections. |
Web Browser (Turn OFF Prefetch)
"Page loading speed improvement" features access sites in the background.
| EEdge | Settings > Cookies and site data OFF "Preload pages for..." |
|---|---|
| CChrome | Settings > Performance OFF "Preload pages" |
| SSafari | Preferences > Search OFF "Preload Top Hit in..." |
| FFirefox | about:config > network.prefetch-next false Change value to "false" |
Generative AI & Data Mining
* Uploading content to cloud-based generative AI may constitute copyright infringement.
Strict Account Management
"Lending your ID to others" or "using someone else's ID" is prohibited under Kyoto University's Information System Usage Regulations.
Posters & Flyers